---
title: "One Year On from GDPR: What’s Changed?"
description: "The General Data Protection Regulation (GDPR) came into effect on May 25, 2018. One year on from the implementation of GDPR, we ask: what’s changed?"
image: https://blog.grantmcgregor.co.uk/hubfs/GDPR-1.png
---
[](https://www.grantmcgregor.co.uk/)
- [Home](https://grantmcgregor.co.uk/)
- About Us
- [Our Story](https://grantmcgregor.co.uk/about-us/our-story)
- [Meet the Team](https://grantmcgregor.co.uk/about-us/meet-the-team)
- [Certifications](https://grantmcgregor.co.uk/about-us/certifications)
- [Careers](https://grantmcgregor.co.uk/about-us/careers)
- IT Support Services
- [IT Support Services](https://grantmcgregor.co.uk/it-support-services)
- [People Centric Support](https://grantmcgregor.co.uk/it-support-services/people-centric-support)
- [Enhanced Security Service](https://grantmcgregor.co.uk/it-support-services/enhanced-security-service)
- Professional IT Services
- [Professional IT Services](https://grantmcgregor.co.uk/professional-it-services)
- [Microsoft 365](https://grantmcgregor.co.uk/professional-it-services/microsoft-365-business-premium)
- [Microsoft Copilot](https://grantmcgregor.co.uk/professional-it-services/microsoft-365-copilot)
- [AI Adoption Services](https://grantmcgregor.co.uk/ai-adoption-services)
- [Microsoft Azure](https://grantmcgregor.co.uk/professional-it-services/microsoft-azure)
- [MDR](https://blog.grantmcgregor.co.uk/mdr-vs-soc-cyber-security-defence)
- [Microsoft Teams Phone](https://grantmcgregor.co.uk/professional-it-services/microsoft-teams-phone)
- [KnowBe4](https://grantmcgregor.co.uk/professional-it-services/knowbe4)
- [DMARC](https://grantmcgregor.co.uk/professional-it-services/dmarc)
- [Enclave Networks](https://grantmcgregor.co.uk/professional-it-services/enclave-networks)
- [Cyber Security](https://grantmcgregor.co.uk/cyber-security)
- Knowledge Hub
- [Case Studies](https://grantmcgregor.co.uk/knowledge-hub/case-studies)
- [Testimonials](https://grantmcgregor.co.uk/knowledge-hub/success-stories)
- [Blog](https://grantmcgregor.co.uk/knowledge-hub/blog)
- [Podcast](https://grantmcgregor.co.uk/knowledge-hub/podcast)
- [Client Area](https://grantmcgregor.co.uk/client-area)
- [Contact us](https://grantmcgregor.co.uk/contact-us)
- [Home](https://grantmcgregor.co.uk/)
- About Us
- [Our Story](https://grantmcgregor.co.uk/about-us/our-story)
- [Meet the Team](https://grantmcgregor.co.uk/about-us/meet-the-team)
- [Certifications](https://grantmcgregor.co.uk/about-us/certifications)
- [Careers](https://grantmcgregor.co.uk/about-us/careers)
- IT Support Services
- [IT Support Services](https://grantmcgregor.co.uk/it-support-services)
- [People Centric Support](https://grantmcgregor.co.uk/it-support-services/people-centric-support)
- [Enhanced Security Service](https://grantmcgregor.co.uk/it-support-services/enhanced-security-service)
- Professional IT Services
- [Professional IT Services](https://grantmcgregor.co.uk/professional-it-services)
- [Microsoft 365](https://grantmcgregor.co.uk/professional-it-services/microsoft-365-business-premium)
- [Microsoft Copilot](https://grantmcgregor.co.uk/professional-it-services/microsoft-365-copilot)
- [AI Adoption Services](https://grantmcgregor.co.uk/ai-adoption-services)
- [Microsoft Azure](https://grantmcgregor.co.uk/professional-it-services/microsoft-azure)
- [MDR](https://blog.grantmcgregor.co.uk/mdr-vs-soc-cyber-security-defence)
- [Microsoft Teams Phone](https://grantmcgregor.co.uk/professional-it-services/microsoft-teams-phone)
- [KnowBe4](https://grantmcgregor.co.uk/professional-it-services/knowbe4)
- [DMARC](https://grantmcgregor.co.uk/professional-it-services/dmarc)
- [Enclave Networks](https://grantmcgregor.co.uk/professional-it-services/enclave-networks)
- [Cyber Security](https://grantmcgregor.co.uk/cyber-security)
- Knowledge Hub
- [Case Studies](https://grantmcgregor.co.uk/knowledge-hub/case-studies)
- [Testimonials](https://grantmcgregor.co.uk/knowledge-hub/success-stories)
- [Blog](https://grantmcgregor.co.uk/knowledge-hub/blog)
- [Podcast](https://grantmcgregor.co.uk/knowledge-hub/podcast)
- [Client Area](https://grantmcgregor.co.uk/client-area)
- [Contact us](https://grantmcgregor.co.uk/contact-us)
[Contact Us](https://grantmcgregor.co.uk/contact-us)
[Back to main](https://grantmcgregor.co.uk/knowledge-hub/blog)
Business News, Cyber Security
# One Year On from GDPR: What’s Changed?
Grant McGregor Team
1 July 2019 • 7 min read
# The General Data Protection Regulation (GDPR) came into effect on May 25, 2018. At the time it was heralded as a major change in the way individuals and organisations will think about – and collect, manage and secure – data.
GDPR was the “four letters that put the fear into firms’ hearts in 2018” according to the Register’s review of the year’s events. But was that fear justified?
One year on from the implementation of GDPR, we ask: what’s changed?
### What’s happened in the year since GDPR came into effect?
Here in the UK, the Information Commissioner’s Office (ICO) is responsible for [enforcing GDPR](https://ico.org.uk/media/about-the-ico/documents/2614992/gdpr-one-year-on-20190530.pdf).
It says it received around 40,000 data protection complaints and 14,000 personal data breach reports between May 25, 2018 and May 1, 2019. Of these personal data breaches, 12,000 cases were closed within that time period. And some 17.5 percent of those cases required action.
The increase in complaints does indicate that GDPR has empowered individuals to take greater control over their own data. And members of the public are now more aware of their privacy rights and the way their data is being used – and misused.
Whether this new understanding is a result of GDPR or the [slow snowballing of the Cambridge Analytica scandal](https://www.ted.com/talks/carole_cadwalladr_facebook_s_role_in_brexit_and_the_threat_to_democracy) – or a combination of the two – is, perhaps, open to debate.
### European regulators warn they are just warming up
Meanwhile, elsewhere in Europe four nations have made public fines under the new regime. These fines have been the most headline-grabbing aspect of GDPR thus far, so it is perhaps surprising that this figure should be so low.
Germany levied a fine of €20,000 against a chat app, Austria levied a fine of €4,800 for the unlawful use of CCTV, and Portugal’s regulator fined a hospital €400,000 for allowing staff unlawful access to data.
The biggest fine levied so far was the €50 million fine the [French regulator CNIL](https://www.cnil.fr/en/cnils-restricted-committee-imposes-financial-penalty-50-million-euros-against-google-llc) laid on Google for lack of transparency, inadequate information and lack of valid consent regarding the personalisation of ads.
In all, around 65,000 data breaches were reported, and 95,000 complaints were filed.
### The increasing clout of European lawmakers
The impact of GDPR isn’t only being felt in Europe. International firms who want to trade in and with Europe have picked up the standards laid down in GDPR as a benchmark for a gold standard in data protection regulation.
Perhaps the best illustration of Europe’s growing clout in this area was the introduction of the [California Consumer Privacy Act](https://www.nytimes.com/2018/08/14/magazine/facebook-google-privacy-data.html). Signed into the State’s Civil Code in June 28, 2018, the Act demonstrates how Europe’s standards are being welcomed and adopted by lawmakers in the home of Big Tech.
California’s legislation was the first time the notion of personal data (as set out by the EU) – and the rights of individuals over their own personal data – was recognised on USA statute books.
As Rebecca Hill wrote in [The Register](https://www.theregister.co.uk/2018/12/26/2018_gdpr_roundup/), there is “growing public pressure to take action against the digital giants they are slowly realising aren’t run by geeks in jeans but, rather, ruthless business people.”
### What can you do to protect your data?
The media and regulator focus on data breaches and their financial penalties has driven information security up the agenda of all businesses, including SMEs. Ensuring you have the right security measures in place, however, isn’t only essential for GDPR compliance – it makes good business sense too.
Over the last year, Grant McGregor has continued to guide SMEs, enterprises and public sector and third-sector organisations through the process of making their data more secure.
At a minimum, these efforts should include:
• Putting in place essential cyber security measures – the Government’s [Cyber Security Essentials scheme](https://www.grantmcgregor.co.uk/it-software-and-solutions/cyber-essentials/) is a good place to start for this.
• Ensuring all operating systems and software used in the organisation are patched and up to date and[running the latest versions](https://www.grantmcgregor.co.uk/2019/urgent-newsflash-end-of-life-for-internet-explorer-10-brought-forward/).
• Creating an [Information Asset Register](https://www.grantmcgregor.co.uk/2018/what-is-an-information-asset-register-and-why-might-it-help-me-be-gdpr-compliant/) to help you manage security risk.
• Understanding the [cyber security threats for your organisation](https://www.grantmcgregor.co.uk/2019/not-faster-than-the-lion/) – including people, technology, process and physical.
• [Securing mobile devices](https://www.grantmcgregor.co.uk/2019/are-you-doing-enough-on-mobile-device-security/) and implementing an effective mobile device policy.
• Reviewing – and, where necessary, beefing up – your [disaster recovery and business continuity](https://www.grantmcgregor.co.uk/2018/how-to-ensure-the-success-of-your-disaster-recovery-and-business-continuity-plans/) plans.
• Training staff to spot common attack vectors, such as [phishing attacks](https://www.grantmcgregor.co.uk/2018/how-do-you-stop-a-phishing-attack/), and how to deal with them.
• Employing [two-factor authentication](https://www.grantmcgregor.co.uk/2019/doubling-up-why-two-factor-authentication-is-your-next-step-in-digital-security/), where appropriate.
### An unwarranted focus on data breaches?
The continued focus on data breaches as the main aspect of GDPR has drawn criticism from some quarters.
The [Federation of Small Businesses (FSB)](https://www.fsb.org.uk/resources/gdpr-one-year-on) says: “The implementation of the GDPR and the Data Protection Act 2018 in May 2018 caused great excitement and confusion in the SME community. Disappointingly, it seemed that the media only focussed on the high new fines and the increased powers of the Information Commissioner’s Office, rather than shedding light on the realistic impact for individuals and organisations.”
Internet law expert Heather Burns says the year since the introduction of GDPR has made it clear “which companies have awakened to ‘privacy by design’ as a powerful tool for user empowerment, and are using GDPR as a launchpad for innovation – and which were only ever interested in using GDPR as a marketing angle for PR campaigns that ended on 26th May.”
It's clear that one year on, integrating the “privacy by design” approach to data management into your operations still offers organisations an opportunity to set themselves apart from the competitors, serve the public better, and gain significant competitive advantage.
### What’s next?
While it may be difficult for small firms to address all the different aspects of GDPR that go beyond improving data security, information officers, and suchlike, should take heart: you are not alone. Earlier this year, it emerged that ICO itself is failing to take its own advice.
In order to address the individual’s right to be informed, ICO recommends organisations produce and distribute a GDPR privacy notice for staff, detailing the way the organisation holds and processes their information. In April 2019, [ICO confirmed it had still not distributed such a document](https://www.theregister.co.uk/2019/04/08/ico_gdpr_privacy_notice/) to its own staff, saying the draft was still under review.
If ICO is still working on all the implications of GDPR, it is fair to say that its implications are still not fully recognised by many organisations in the UK.
If you aren’t sure about your responsibilities under GDPR, Grant McGregor consultants can help. Contact us [here](https://www.grantmcgregor.co.uk/contact-us/).
### Developing the GDPR agenda in 2019
The [UK Information Commissioner Elizabeth Denham](https://ico.org.uk/about-the-ico/news-and-events/blog-gdpr-one-year-on/) marked the one-year anniversary with a blog post in which she set out her vision for how GDPR will evolve through 2019/20.
She said, “With the initial hard work of preparing for and implementing the GDPR behind us, there are ongoing challenges of operationalising and normalising the new regime. This is true for businesses and organisations of all sizes. A key area of work for my office during 2019/20 will be to support all parts of the UK business community, from the smallest SMEs to the biggest boardrooms, to deliver what is needed. Where the law requires it, I want to see Data Protection Officers (DPOs) embedded and supported in their respective organisations by senior management.
The focus for the second year of the GDPR must be beyond baseline compliance – organisations need to shift their focus to accountability with a real evidenced understanding of the risks to individuals in the way they process data and how those risks should be mitigated.”
We look forward to seeing how efforts to embed rights and enforce the regulation progress over the coming year.
If you’d like help embedding GDPR best practice in your organisation, Grant McGregor can help. Call us today on 080 164 4142.
Grant McGregor Team
1 July 2019 • 7 min read
## Recent Posts
### Shadow AI: Is Your Business Ready for AI Adoption?
Understand shadow AI's impact on your business. Discover how to assess risks, improve processes, and adopt AI securely w...
[Read More](https://blog.grantmcgregor.co.uk/shadow-ai-is-your-business-ready-for-ai-adoption)
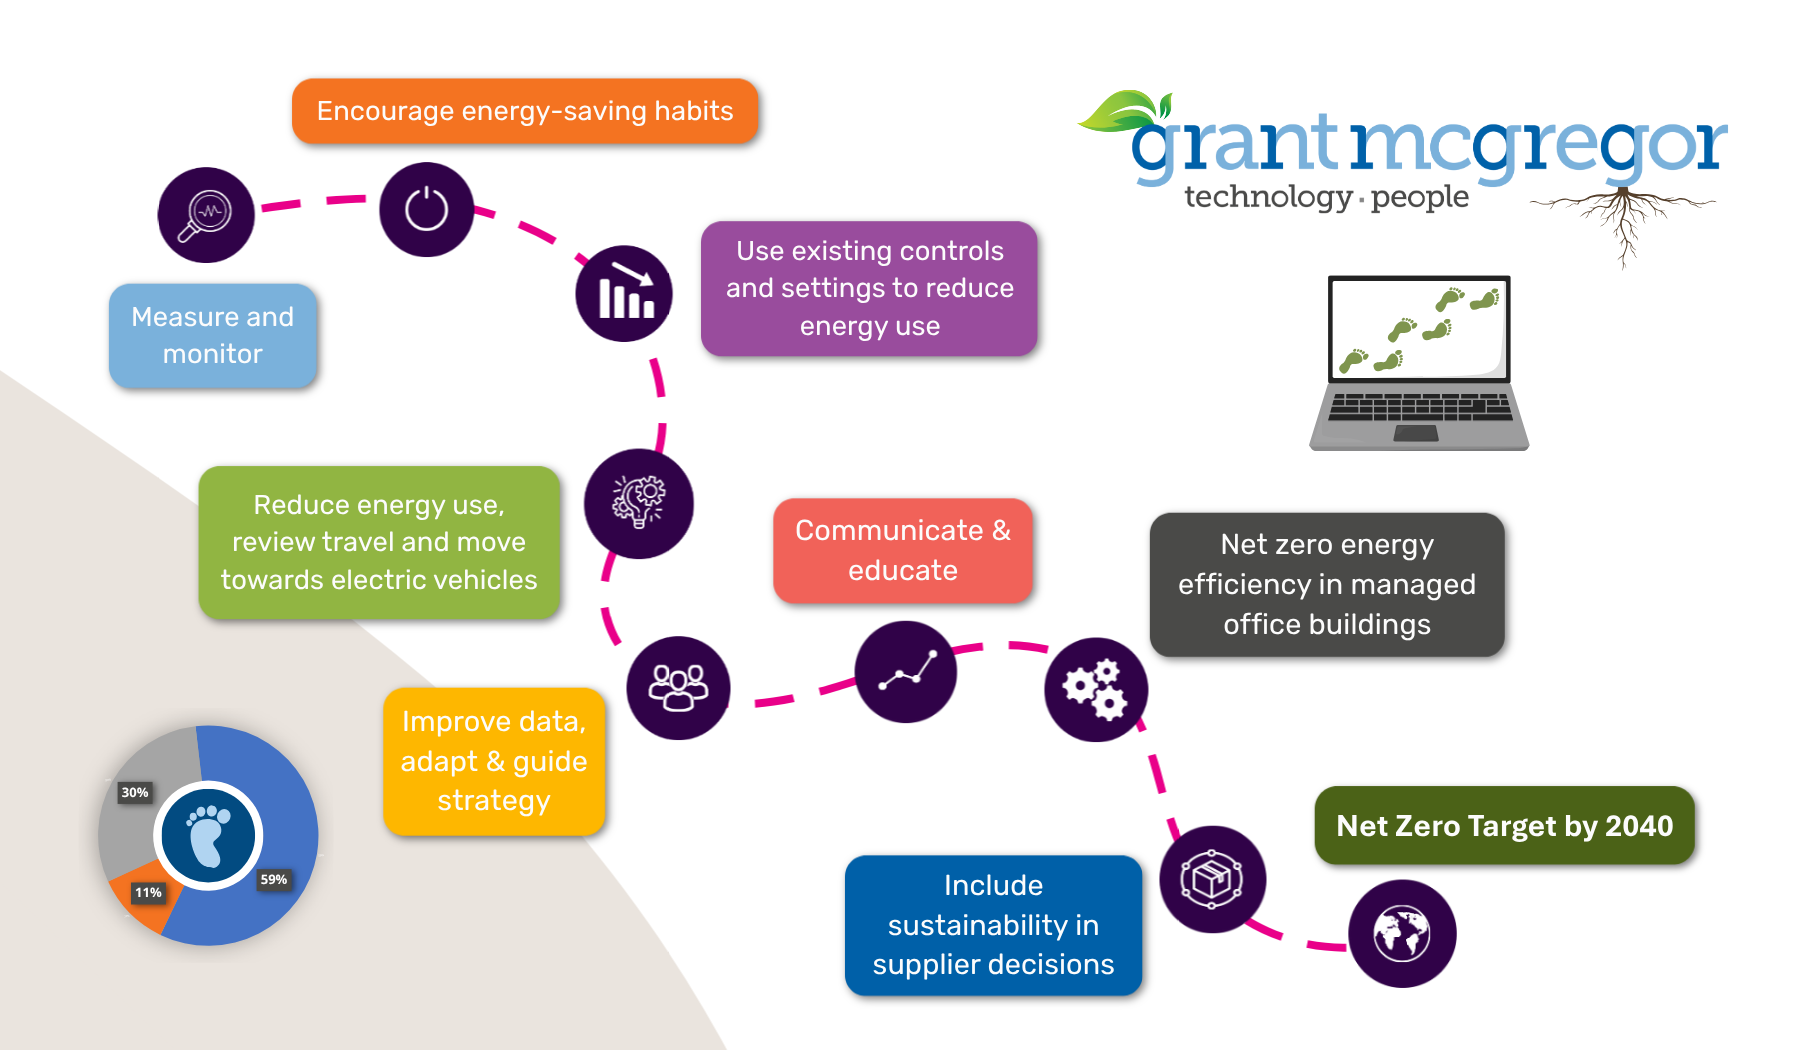
### Our Net Zero Target for 2040: What Can We Change?
From company vehicles and travel to suppliers and technology, see how Grant McGregor is working towards its net zero tar...
[Read More](https://blog.grantmcgregor.co.uk/our-net-zero-target-for-2040-what-can-we-change)
### What Is Penetration Testing? A Guide for Businesses
Learn what penetration testing is, how it works, what the report should include and when your business should consider a...
[Read More](https://blog.grantmcgregor.co.uk/what-is-penetration-testing-a-guide-for-businesses)
### Grant McGregor Recognised as a Leading Global MSP in the 2026 MSP 501
Grant McGregor has been named a Top Global Managed Service Provider in the 2026 MSP 501, ranking #1 Scotland-based MSP a...
[Read More](https://blog.grantmcgregor.co.uk/grant-mcgregor-recognised-as-a-leading-global-msp-in-the-2026-msp-501)
Union
## Empower your business with secure, expert-led solutions.
Talk to us about people-focused technology that drives results.
[Start a conversation](https://grantmcgregor.co.uk/contact-us)


Premium IT Services Tailored for Leading Brands
[Follow us on LinkedIn](https://www.linkedin.com/company/grant-mcgregor-ltd/) [Follow us on Facebook](https://www.youtube.com/itgrantmcgregor) [Follow us on Facebook](https://www.facebook.com/grantmcgregorltd/) [Follow us on Twitter](https://x.com/GrantMcGregorIT)
Quick Links
- [Home](https://grantmcgregor.co.uk)
- [About us](https://grantmcgregor.co.uk/about-us/our-story)
- [Knowledge Hub](https://grantmcgregor.co.uk/knowledge-hub/blog)
- [Contact us](https://grantmcgregor.co.uk/contact-us)
Services
- [People Centric Support](https://grantmcgregor.co.uk/it-support-services/people-centric-support)
- [Enhanced Security Service](https://grantmcgregor.co.uk/it-support-services/enhanced-security-service)
- [Professional IT Services](https://grantmcgregor.co.uk/professional-it-services)
- [Cyber Security](https://grantmcgregor.co.uk/cyber-security)
Edinburgh – Chesterfield

[0131 603 7910](tel:+441316037910)

[info@grantmcgregor.co.uk](mailto:info@grantmcgregor.co.uk)

**Main Office:**
The Merchants' Hall,
22 Hanover St,
Edinburgh EH2 2EP
© 2026
Grant McGregor. All rights reserved.
[Privacy and Cookie Policy](https://blog.grantmcgregor.co.uk/hubfs/UsefulDownloads/Policies/GRMC-SEC-Privacy-and-Cookie-Policy.pdf)
```json
{
"@context" : "https://schema.org",
"@type" : "BlogPosting",
"author" : {
"@type" : "Person",
"name" : "Grant McGregor Team",
"url" : "https://blog.grantmcgregor.co.uk/author/grmc-team"
},
"dateModified" : "2020-10-22T11:08:49.710Z",
"datePublished" : "2019-07-01T09:58:08.000Z",
"headline" : "One Year On from GDPR: What’s Changed?",
"image" : [ "https://blog.grantmcgregor.co.uk/hubfs/GDPR-1.png" ],
"mainEntityOfPage" : {
"@id" : "https://blog.grantmcgregor.co.uk/2019/one-year-on-from-gdpr-whats-changed",
"@type" : "WebPage"
},
"publisher" : {
"@type" : "Organization",
"logo" : {
"@type" : "ImageObject",
"url" : "https://blog.grantmcgregor.co.uk/hubfs/GRMC_blue_logo.svg"
},
"name" : "Grant McGregor"
}
}
```
```json
{
"@context" : "https://schema.org",
"@id" : "https://grantmcgregor.co.uk/",
"@type" : "LocalBusiness",
"address" : {
"@type" : "PostalAddress",
"addressCountry" : "GB",
"addressLocality" : "Edinburgh",
"postalCode" : "EH2 2EP",
"streetAddress" : "22 Hanover Street"
},
"geo" : {
"@type" : "GeoCoordinates",
"latitude" : 55.9526313,
"longitude" : -3.1970679
},
"image" : "https://grantmcgregor.co.uk/hubfs/GRMC_blue_logo.svg",
"name" : "Grant McGregor",
"openingHoursSpecification" : {
"@type" : "OpeningHoursSpecification",
"closes" : "18:00",
"dayOfWeek" : [ "Monday", "Tuesday", "Wednesday", "Thursday", "Friday" ],
"opens" : "08:00"
},
"sameAs" : [ "https://www.facebook.com/grantmcgregorltd/", "https://x.com/GrantMcGregorIT", "https://www.youtube.com/itgrantmcgregor", "https://www.linkedin.com/company/grant-mcgregor-ltd/" ],
"telephone" : "+441316037910",
"url" : "https://grantmcgregor.co.uk/"
}
```